Authoritative DNS for your domains
Full control over your zones — without babysitting a single name server.
Delegate your domains to our authoritative DNS servers and manage every record from a clean web UI — with DNSSEC and fine-grained team permissions.
Why Dremaxx as authoritative DNS
Geo-distributed name servers keep your domains reachable — always.
One-click DNSSEC signing with fully managed keys.
Lean, optimised nameservers deliver consistently low response times.
Organisations, members and roles for shared zones.
How to use authoritative DNS
Create account
Sign up free and confirm your email — takes a minute.
Create zone
Add your domain as a zone and configure the records you need.
Delegate NS
Point your registrar to our name servers – done.
See the console in action
A look inside the management console — organisations, zones and records in one clean dashboard.
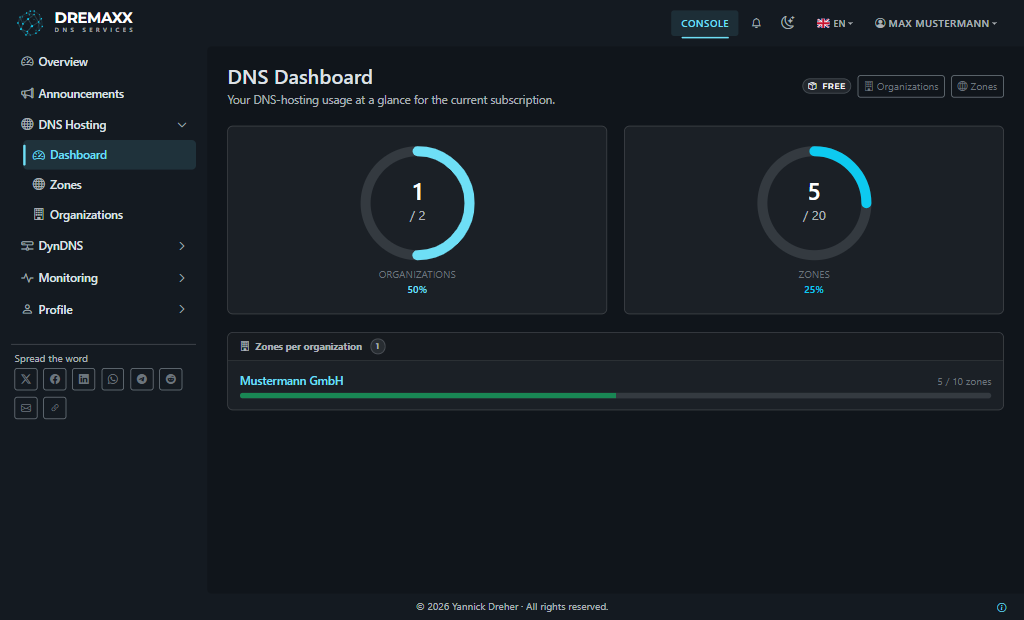
Your organisations, zones and plan limits at a glance.
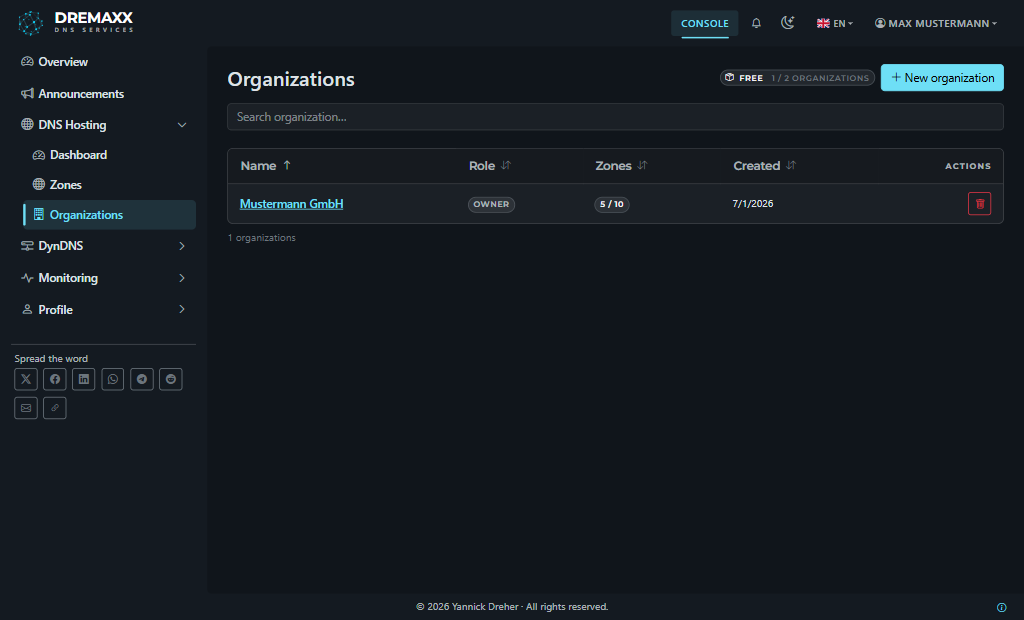
Group zones into organisations and manage members and roles.
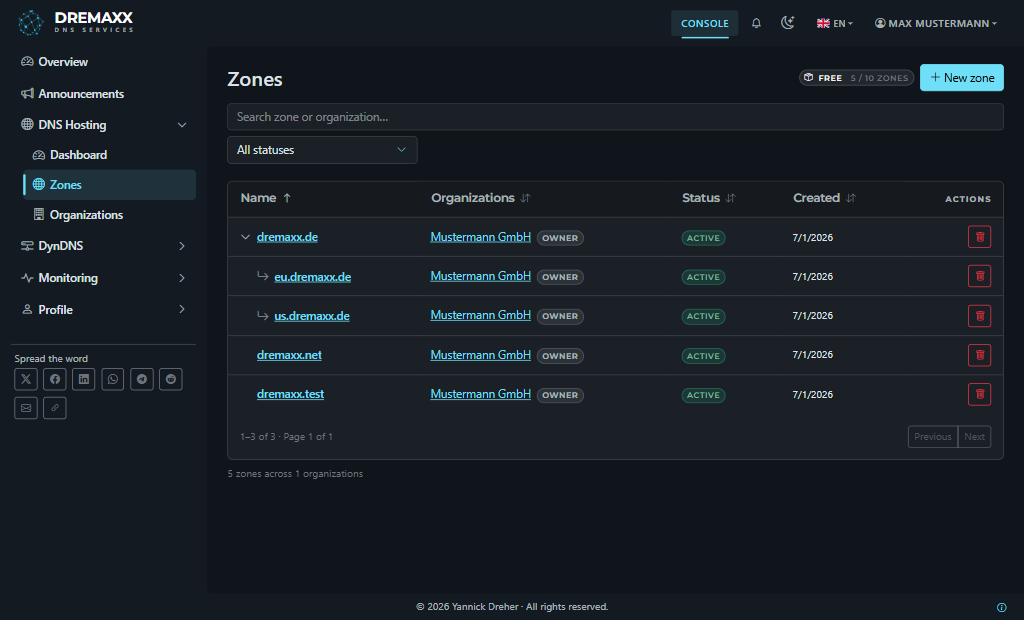
All your zones with status, DNSSEC and quick access in one list.
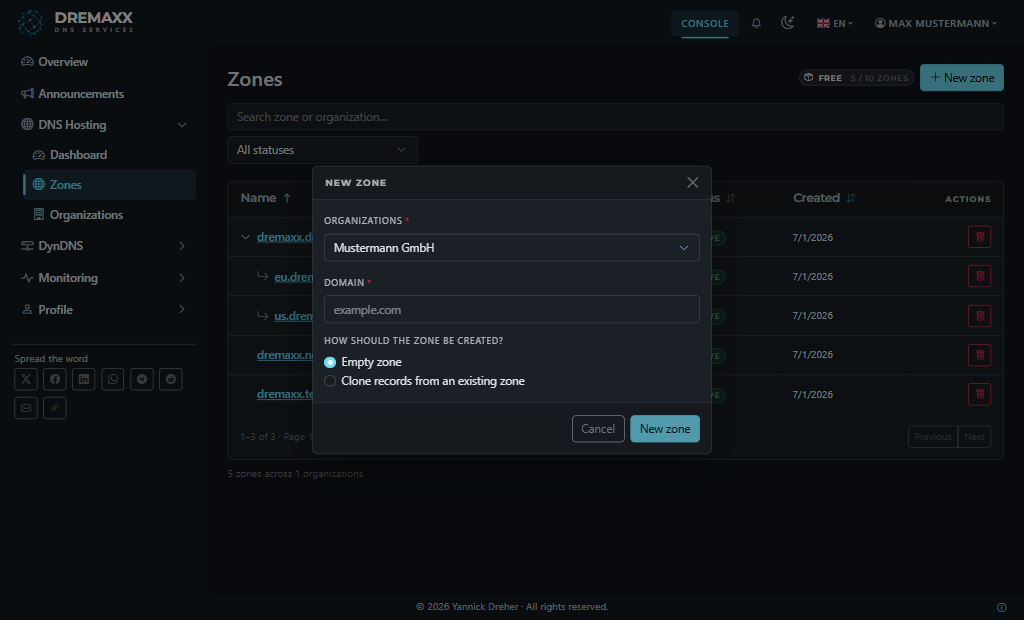
Add a new zone in seconds — empty or cloned from an existing one.
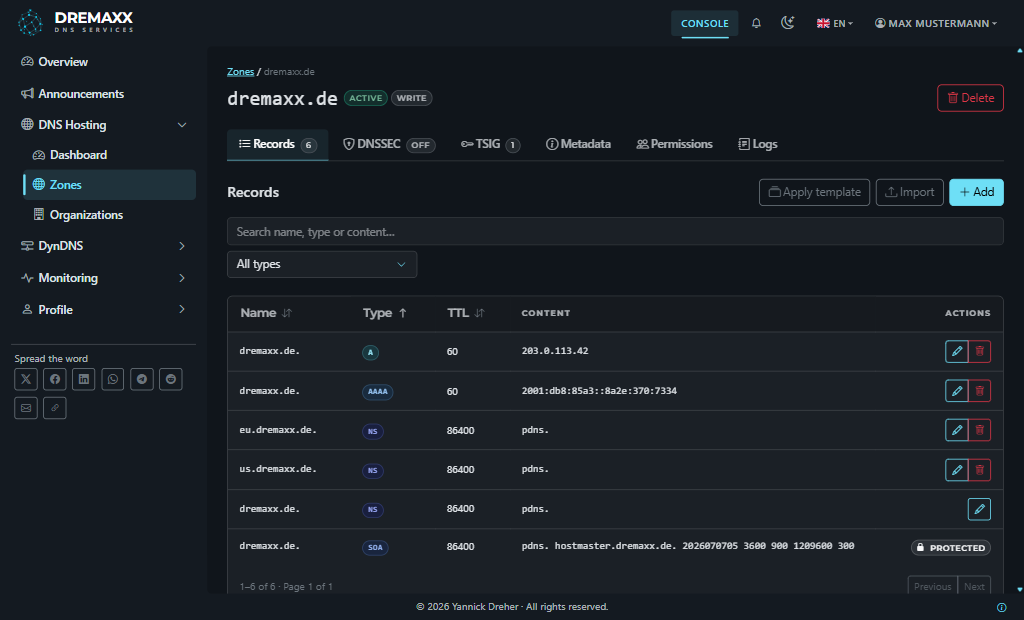
Edit records, DNSSEC and TSIG keys in a focused, fast editor.
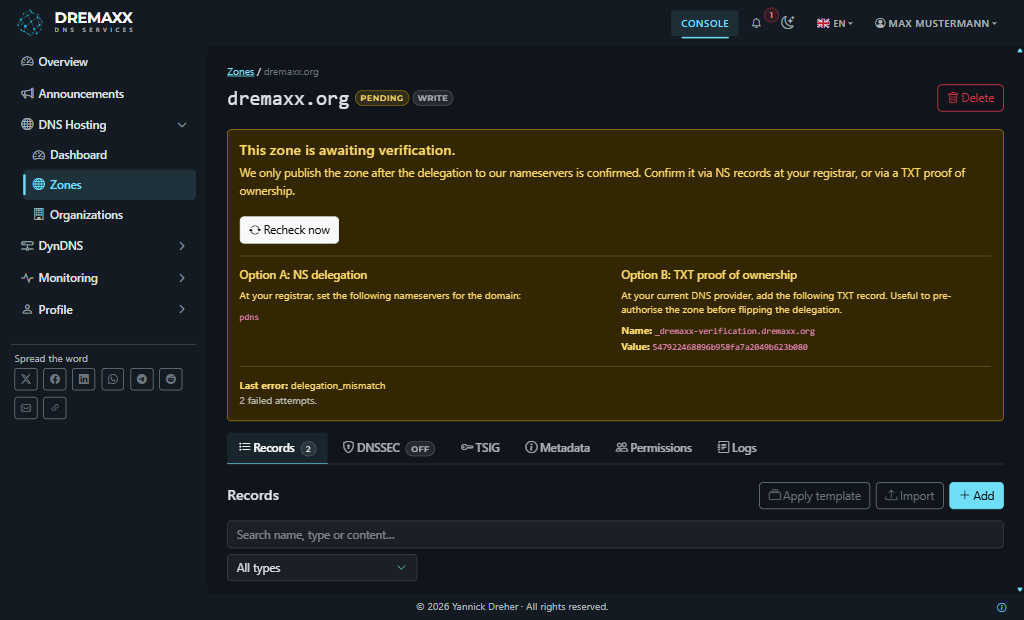
Follow delegation and verification status while a new zone goes live.
Full control over your zones
Run your zones like you would on your own name server — without the server maintenance.
Create A, AAAA, CNAME, MX, TXT, SRV and 14 more record types via the web editor or BIND import.
Add extra NS records on top of our apex NS — ideal for your own secondaries or mixed multi-provider deployments.
AXFR zone transfers to your own secondaries are automatically allowed as soon as their NS records are in the zone.
Enable signing with managed KSK/ZSK — including DS records to hand to your registrar.
Upload, validate and apply existing zone files in classic BIND format.
Grant read or write access per zone to org members — on top of owner/admin/member roles.
Every change to zones, records, DNSSEC and permissions is recorded in a verifiable audit log.
Changes from other tabs or team members appear in the UI instantly.
Manage zones and records by conversation
Connect your AI assistant to the DNS hosting endpoint and let it work with organizations, zones, records and DNSSEC — through the same permission checks and the same audit log as the console.
https://dremaxx.de/api/mcp/dns-hosting- Add an A record for example.com pointing to 203.0.113.10.
- Which of my zones are still running without DNSSEC?
- Show me the recent changes to the example.com zone.
Your limits, not the AI'sEvery call goes through the same permission checks and the same audit log as the console. An assistant can never do more than you granted its token — and you can revoke it at any time with one click.
Supported record types
All record types you can create via the web editor, grouped by purpose.
Addresses
AIPv4 address of a hostAAAAIPv6 address of a host
Aliases & delegation
CNAMEAlias for another nameALIASCNAME-like alias at the zone apexDNAMERedirect an entire namespaceNSDelegate a subzonePTRReverse lookup (address to name)
MXMail servers for the domainSPFSender policy (legacy; TXT preferred)TXTFree text: SPF, DKIM, DMARC, verifications
Security
CAACertificate authorities allowed to issueDSDNSSEC key reference for subzonesTLSADANE: bind a certificate to a TLS serviceSSHFPSSH host key fingerprint
Services & other
SRVService with host, port and prioritySVCBService binding with parametersHTTPSHTTPS endpoint with ALPN, ECH and moreNAPTRRule-based name rewriting (ENUM, SIP)URIURI for a serviceLOCGeographic location
SOA is managed by the platform. Apex NS records of our servers are protected, but you can add additional NS records on top.
Ready for your first zone?
Set up your first zone in minutes — no server maintenance, ever.
Sign up freeRecently reported
Never miss one
Get an email whenever there is something to report about dns-hosting — incidents, maintenance and news. Changeable at any time, cancellable at any time.